Coreitech's AI SOC monitors your Microsoft Entra ID in real time — sign-ins, password resets, privilege escalation, and audit events. AI detects anomalies in under 60 seconds; UK-based human analysts investigate every alert. From £15/user/month. 0203 834 9728.
AI SOC
SERVICES
REAL-TIME · ENTRA ID · UK
Coreitech's AI-powered Security Operations Centre monitors your Microsoft Entra ID in real time. AI detects anomalous sign-ins, password resets, and privilege escalations in under 60 seconds — UK-based human SOC analysts investigate every alert, 24/7.
From event to containment in minutes — not hours or days.
CORINA AI SOC HUNTER
Autonomous. Relentless. Always Hunting. Corina is our AI-powered SOC Hunter — continuously monitoring, detecting, and neutralising threats across your environment 24/7/365.
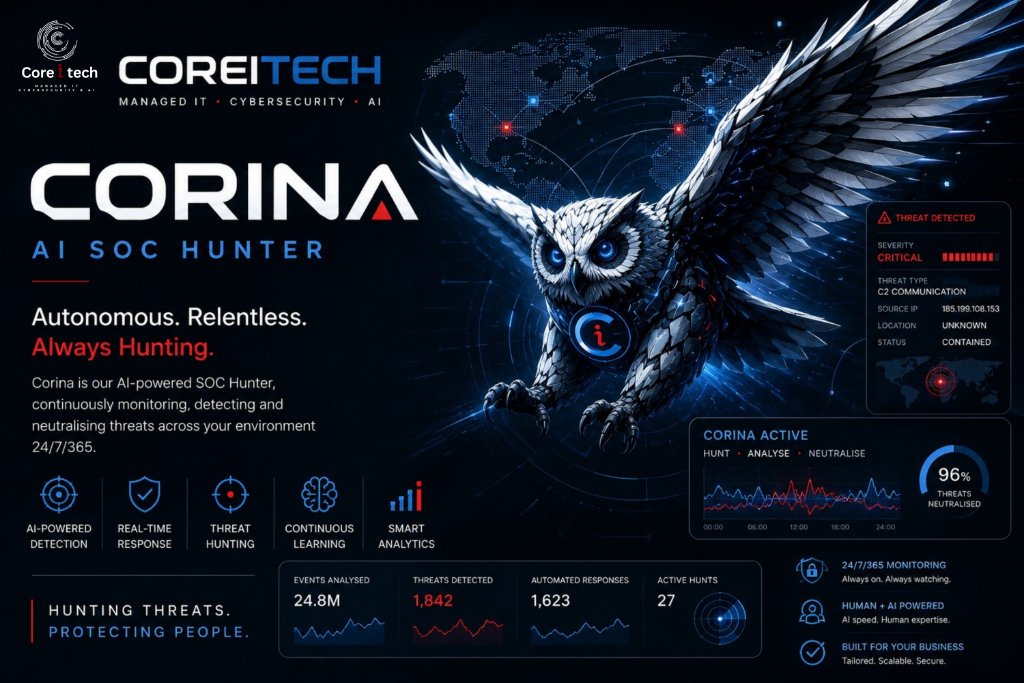
HUNTING THREATS. PROTECTING PEOPLE.
What is an AI-powered
Security Operations Centre?
An AI SOC (AI Security Operations Centre) combines artificial intelligence with human security analysts to monitor, detect, and respond to cyber threats in real time. Unlike a traditional SOC that relies on manual log review and static rules, an AI SOC uses machine learning to ingest every security event, baseline normal behaviour per user, and surface only genuine anomalies.
Coreitech's AI SOC is Microsoft Entra ID native. We monitor every sign-in, audit log entry, and identity risk signal in your Entra ID tenant — from password resets to privilege escalation — and alert our UK-based SOC analysts in under 60 seconds when the AI detects something anomalous.
The result: threats are detected and investigated in near real time, not hours or days later. Alert fatigue is eliminated — analysts only see genuine threats. And human judgement is preserved — AI surfaces, humans decide and respond.
AI SOC vs Traditional SOC
Every Entra ID event —
monitored and AI-analysed
Our AI SOC monitors every security and audit event in your Microsoft Entra ID tenant. Nothing is missed — every signal is ingested, baselined, and analysed in real time.
Sign-In Activity
Every Entra ID authentication — successful and failed. AI flags anomalous sign-ins, brute-force patterns, and legacy authentication attempts in real time.
Impossible Travel
AI detects sign-ins from geographically impossible locations within unrealistic timeframes — a classic compromised-account indicator.
Privilege Escalation
Role assignments, admin group changes, and consent grants monitored continuously. Alert fired the moment a user gains unexpected elevated access.
Password Resets
Every password reset, change, and self-service password registration tracked. Anomalous reset patterns flagged for analyst investigation immediately.
MFA Changes
MFA registration, bypass, and fraud reports monitored. If a user suddenly deregisters an MFA method, our AI alerts before damage is done.
Conditional Access
Conditional access policy changes, new policy creation, and policy failures tracked — so a misconfiguration never becomes a breach.
Audit Log Events
Every audit event in Entra ID — directory changes, app registrations, service principal activity, group membership changes — monitored and correlated.
Risky Users & Sign-Ins
Entra Identity Protection risk events — leaked credentials, unfamiliar sign-in properties, infected devices — enriched with AI context for triage.
From Entra ID event to
threat contained — in minutes
Entra ID Integration
We connect to your Microsoft Entra ID tenant via Microsoft Graph API and Azure Monitor. No agents, no infrastructure — native integration with read-only audit permissions. Live within 24 hours.
AI Continuous Monitoring
Our AI engine ingests every sign-in event, audit log entry, and identity risk signal in real time. Machine learning baselines normal behaviour for every user, then flags deviations instantly.
Real-Time Alerting
When AI detects a threat — anomalous sign-in, privilege escalation, password reset spike, impossible travel — an alert is generated in under 60 seconds with full context attached.
Human Analyst Investigation
Our UK-based SOC analysts review every AI-flagged alert in near real time. They triage, investigate, and escalate — filtering false positives so you only see genuine threats.
Response & Containment
For confirmed threats, analysts initiate response — force sign-out, reset credentials, revoke sessions, disable accounts — and notify your team with a clear remediation summary.
Why AI SOC beats
traditional SOC monitoring
| Factor | Coreitech AI SOC | Traditional SOC |
|---|---|---|
| Alert speed | <60 seconds — AI processes events in real time | Minutes to hours — batch processing or manual review |
| Alert volume | AI filters noise — analysts see only genuine threats | Thousands of raw alerts — alert fatigue and missed threats |
| Coverage | Every sign-in, audit event, and identity signal — 24/7 | Limited log sources, gaps outside business hours |
| Investigation | AI enriches alerts with context before analyst review | Analysts spend hours gathering context manually |
| False positives | AI learns normal behaviour — false positives reduced 90%+ | High false positive rate causes alert fatigue |
| Human expertise | UK-based SOC analysts investigate every flagged alert | Often offshore or automated-only with no human triage |
Why businesses choose
Coreitech's AI SOC
Near real-time threat detection
AI processes Entra ID events as they happen. From suspicious sign-in to analyst investigation in under 60 seconds — not hours or days.
AI filters alert noise
Traditional SOC dashboards drown analysts in thousands of raw alerts. Our AI baselines normal behaviour and surfaces only genuine anomalies — reducing false positives by 90%+.
Human-in-the-loop investigation
AI doesn't replace analysts — it empowers them. Every flagged alert is investigated by a UK-based SOC analyst who adds context, triage, and response decisions.
Comprehensive Entra ID coverage
Sign-ins, audit logs, identity protection, conditional access, MFA, password resets, privilege changes — everything monitored, nothing missed.
24/7/365 coverage
AI never sleeps. Our SOC operates around the clock — threats detected and investigated at 3am on a Sunday, not Monday morning.
Faster containment
When a threat is confirmed, analysts can force sign-out, revoke sessions, and disable accounts within minutes — limiting blast radius dramatically.
AI SOC monitoring for
your sector
AI SOC —
your questions answered
Q.What is an AI SOC?
An AI SOC (AI Security Operations Centre) combines artificial intelligence with human security analysts to monitor, detect, and respond to cyber threats in real time. Unlike a traditional SOC that relies on manual log review and pre-set rules, an AI SOC uses machine learning to ingest every security event, baseline normal behaviour, and surface only genuine anomalies for human investigation. Coreitech's AI SOC specifically monitors Microsoft Entra ID — every sign-in, audit log entry, and identity risk signal — alerting our UK-based SOC analysts in under 60 seconds so threats are investigated and contained before damage is done.
Q.How does AI SOC monitoring work with Microsoft Entra ID?
Coreitech's AI SOC connects to your Microsoft Entra ID tenant via Microsoft Graph API and Azure Monitor with read-only permissions. The AI engine ingests every sign-in event (successful and failed), audit log entry, identity protection risk event, conditional access policy change, MFA registration, password reset, and privilege escalation in real time. Machine learning baselines normal behaviour for each user, then flags deviations — impossible travel, brute-force patterns, anomalous password resets, unexpected admin role assignments — for human analyst investigation. No agents or infrastructure required; integration is typically live within 24 hours.
Q.What is the difference between an AI SOC and a traditional SOC?
A traditional SOC relies on SIEM rules, manual log review, and pre-set thresholds — generating thousands of raw alerts that cause alert fatigue, with analysts spending hours gathering context. An AI SOC uses machine learning to process every event in real time, baseline normal behaviour per user, and filter false positives automatically — reducing alert noise by 90%+. AI enriches each alert with context before a human analyst even sees it. The result: threats detected in under 60 seconds (vs hours), genuine alerts investigated by analysts (vs drowning in noise), and 24/7 coverage (vs gaps outside business hours). Coreitech's AI SOC keeps human analysts in the loop — AI surfaces threats, humans investigate and respond.
Q.How fast are AI SOC alerts?
Coreitech's AI SOC generates alerts in under 60 seconds from the triggering event. The AI ingests Entra ID events in real time via Microsoft Graph API, analyses them against learned behavioural baselines, and fires an alert immediately when an anomaly is detected. The alert is then queued for human analyst investigation — typically picked up within minutes, 24/7. This compares to traditional SOC models where alerts can take hours or even days to surface due to batch processing, manual review queues, or out-of-hours coverage gaps.
Q.What Entra ID events does the AI SOC monitor?
Coreitech's AI SOC monitors every Entra ID security and audit event, including: (1) all sign-in activity — successful, failed, and interactive; (2) impossible travel and anomalous location detection; (3) password resets, changes, and self-service registrations; (4) MFA registrations, bypasses, and fraud reports; (5) privilege escalation — role assignments, admin group changes, consent grants; (6) conditional access policy changes and failures; (7) directory changes — app registrations, service principal activity, group membership; (8) Entra Identity Protection risk events — leaked credentials, unfamiliar sign-in properties, risky users. Every event is correlated and analysed by AI for anomalies.
Q.Does the AI SOC replace human security analysts?
No. Coreitech's AI SOC is a human-in-the-loop model — AI empowers analysts, it doesn't replace them. The AI handles the volume problem: ingesting millions of events, baselining normal behaviour, filtering false positives, and enriching alerts with context. Human SOC analysts handle the judgement problem: investigating flagged alerts, determining whether a threat is genuine, deciding on response actions, and containing confirmed threats. This combination delivers both speed (AI) and accuracy (human judgement) — neither works as well alone.
Q.How much does AI SOC monitoring cost?
AI SOC monitoring pricing depends on user count and required response SLAs. Coreitech offers AI SOC monitoring from £15–£35 per user per month, which includes real-time Entra ID monitoring, AI-powered alerting, 24/7 human analyst investigation, and incident response. For a 50-user business that's £750–£1,750/month — significantly less than building an in-house SOC (which costs £500,000+ annually for a minimal 3-analyst team providing only business-hours coverage). Contact us for a tailored quote based on your environment size and risk profile.
Q.Can the AI SOC respond to threats or just alert on them?
Coreitech's AI SOC provides full response capability, not just alerting. When a threat is confirmed by a human analyst, we can initiate immediate containment actions within your Entra ID tenant: force user sign-out, revoke active sessions, reset credentials, disable accounts, and revoke OAuth grants. Response actions are agreed with you in advance via an incident response playbook, so analysts can act immediately without waiting for approval — critical when minutes matter during an active attack.
Q.Do I need Microsoft 365 or Azure to use the AI SOC?
You need a Microsoft Entra ID tenant (included with any Microsoft 365 business plan or available standalone). Coreitech's AI SOC connects via Microsoft Graph API with read-only audit permissions — no agents, no servers, no additional infrastructure. If you use Microsoft 365 for email, Teams, SharePoint, or any Microsoft cloud service, you already have Entra ID. The AI SOC monitors that environment natively. For organisations using Google Workspace or other identity providers, contact us to discuss integration options.
Q.How is AI SOC different from SIEM or EDR?
SIEM (Security Information and Event Management) is a log aggregation platform that requires rules, tuning, and manual analysis — it generates raw alerts without context. EDR (Endpoint Detection and Response) monitors individual devices for malware and process-level threats. An AI SOC is different: it focuses on identity-level threats (who is signing in, from where, doing what) rather than device-level threats, uses AI to filter noise automatically rather than relying on rules, and includes human analysts who investigate every flagged alert. Coreitech's AI SOC complements EDR — together they provide comprehensive coverage of both identity threats (Entra ID) and endpoint threats (devices).
See your AI SOC
in action
Book a 30-minute demo. We'll connect to your Entra ID tenant and show you real-time threat detection, AI alerting, and human analyst investigation — live.