Coreitech's AI SOC Platform is an enterprise-grade security operations centre built on Microsoft Azure with a 99.9% uptime SLA. AI correlates telemetry across Entra ID, Defender, Exchange & Intune — enriched with real-time threat intelligence from Microsoft TI and CISA KEV. Alerts in under 60 seconds, investigated by UK-based analysts 24/7. Zero infrastructure — live in 24 hours. From £15/user/month. 0203 834 9728.
AI SOC
PLATFORM
ENTERPRISE-GRADE · THREAT INTELLIGENCE
An enterprise-grade AI Security Operations Centre built on Microsoft Azure. AI correlates millions of signals across identity, endpoint, email, and network telemetry — enriched with real-time threat intelligence. Alerts in under 60 seconds. UK-based analysts investigate every alert, 24/7/365.
Enterprise-grade architecture — no agents, no SIEM, no infrastructure.
CORINA AI SOC HUNTER
Autonomous. Relentless. Always Hunting. Corina is our AI-powered SOC Hunter — continuously monitoring, detecting, and neutralising threats across your environment 24/7/365.
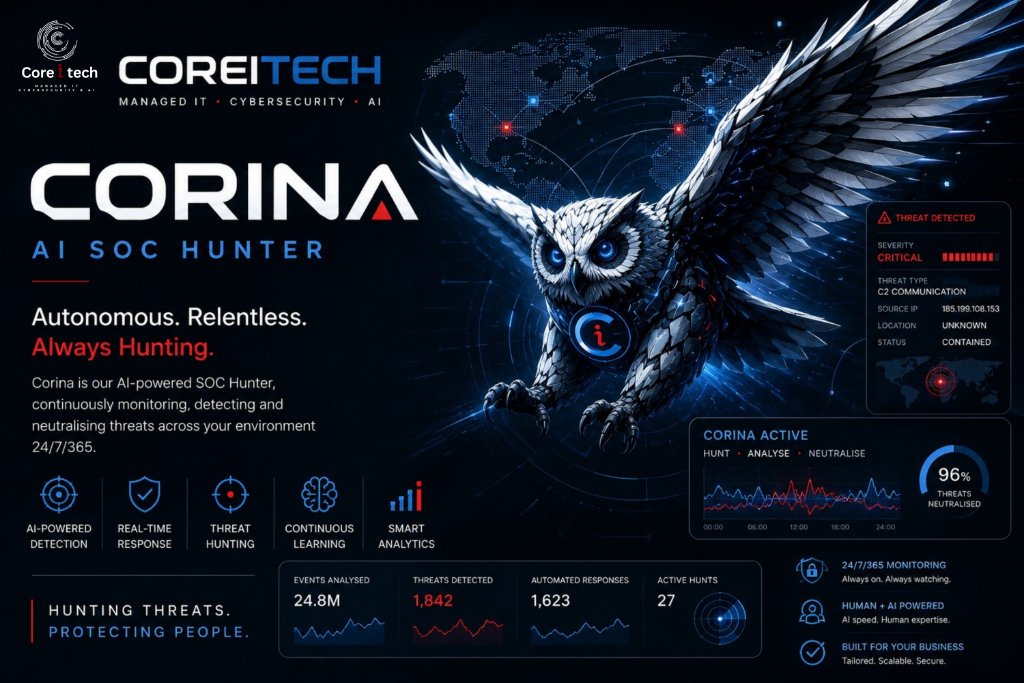
HUNTING THREATS. PROTECTING PEOPLE.
Enterprise-grade architecture,
built for scale and stability
Every component of the AI SOC platform is designed for enterprise-grade reliability — from the data pipeline to the threat intelligence enrichment to the automated response playbooks.
AI Threat Correlation Engine
Machine learning correlates millions of signals across identity, endpoint, email, and network telemetry — surfacing only genuine threats with full attack-chain context. No more alert fatigue.
Threat Intelligence Integration
Real-time feeds from Microsoft Threat Intelligence, CISA KEV database, and commercial TI sources enrich every alert with known adversary TTPs, IOCs, and CVE exploit status.
Behavioural Baselining
AI learns normal behaviour for every user, device, and service — then flags deviations instantly. Anomalous sign-ins, mass file downloads, or privilege escalation detected in under 60 seconds.
Multi-Layer Telemetry
Entra ID sign-ins, Microsoft Defender alerts, Exchange mail flow, Intune device compliance, and conditional access logs — all ingested, correlated, and analysed in a single pipeline.
Enterprise-Grade Data Pipeline
Built on Microsoft Azure infrastructure with 99.9% SLA. Events ingested via Microsoft Graph API and Azure Monitor — no agents, no on-prem infrastructure, no capacity planning.
Automated Playbooks
Pre-built response playbooks execute on confirmed threats: force sign-out, revoke sessions, disable accounts, quarantine devices — with full audit trail and human approval gates.
Built on Azure —
99.9% SLA, zero infrastructure
The platform runs on Microsoft Azure infrastructure with multi-region failover and real-time streaming architecture. No SIEM appliances, no log collectors, no capacity planning. Just native Microsoft Graph API integration.
Built on Azure infrastructure with multi-region failover. No single point of failure in the ingestion, processing, or alerting pipeline.
From event ingestion to analyst-visible alert in under 60 seconds. No batch processing delays — real-time streaming architecture.
AI monitors around the clock. UK-based SOC analysts investigate every flagged alert — 3am Sunday gets the same response as 11am Wednesday.
No agents to deploy, no SIEM to tune, no servers to maintain. Native Microsoft Graph API integration with read-only permissions — live within 24 hours.
Real-time threat intelligence,
built into every alert
Every alert is enriched with threat intelligence before a human analyst sees it — so analysts spend time investigating, not gathering context. Intelligence from Microsoft's global network, CISA, and sector-specific feeds.
Microsoft Threat Intelligence
Microsoft's global threat intelligence network — trillions of signals daily from 1.4+ billion Windows devices, Exchange Online, and Azure.
CISA KEV Database
Known Exploited Vulnerabilities catalogue from CISA. Every alert cross-referenced against actively exploited CVEs in the wild.
Microsoft Defender Threat Intelligence
Adaptor TTPs, IOCs, and threat actor profiles from Microsoft's incident response and security research teams.
Entra ID Identity Protection
Real-time risk events — leaked credentials, unfamiliar sign-in properties, token theft, and impossible travel patterns.
Microsoft Sentinel Analytics
Fusion detection rules that correlate low-fidelity signals across multiple data sources into high-fidelity multi-stage attack detections.
Custom Threat Feeds
Sector-specific intelligence for financial services, legal, healthcare, and public sector — tailored to the threats targeting your industry.
Why our AI SOC platform beats
a traditional managed security service
| Factor | Coreitech AI SOC Platform | Traditional MSSP |
|---|---|---|
| Threat detection speed | <60 seconds — real-time AI streaming | 5–30 minutes — batch SIEM processing |
| Alert quality | AI correlates & enriches — 90%+ fewer false positives | Raw SIEM alerts — analysts drown in noise |
| Data sources | Entra ID, Defender, Exchange, Intune — unified pipeline | SIEM-only — requires agent deployment & log forwarding |
| Infrastructure required | Zero — native Graph API integration, live in 24h | SIEM appliance, log collectors, network sensors — weeks to deploy |
| Threat intelligence | Microsoft TI + CISA KEV + sector feeds — built in | Often an add-on or requires separate TI subscription |
| Analyst coverage | UK-based SOC analysts — every alert investigated | Often offshore or follow-the-sun with handoff gaps |
| Response automation | Playbooks execute on confirmation — sign-out, revoke, disable | Manual response — analyst opens ticket, waits for client approval |
| Pricing model | From £15/user/month — all-inclusive, no add-ons | Per-GB ingestion + per-alert + per-analyst-hour — unpredictable |
FCA-regulated wealth management firm
detected compromised admin account in 47 seconds
From anomalous sign-in to analyst-visible alert. The AI detected a sign-in from Warsaw 3 minutes after a London sign-in — geographically impossible.
Data exfiltrated. The automated playbook revoked the session and disabled the account before the attacker could access client portfolios.
Incident response cost. The threat was contained by the platform's automated playbooks — no external IR team required, no downtime.
"The AI SOC platform detected a compromised admin account within 47 seconds — before the attacker could access any client data. The automated response playbook revoked the session and disabled the account instantly. Our previous MSSP would have taken 20+ minutes to even see the alert."
AI SOC platform for
your sector
Threat intelligence feeds and response playbooks tailored to the specific adversaries and compliance requirements of your industry.
AI SOC Platform —
your questions answered
Q.What makes Coreitech's AI SOC platform enterprise-grade?
Coreitech's AI SOC platform is built on Microsoft Azure infrastructure with a 99.9% uptime SLA and multi-region failover — no single point of failure in the ingestion, processing, or alerting pipeline. The platform ingests telemetry via native Microsoft Graph API integration (no agents or on-prem infrastructure), processes events in real-time using streaming architecture (not batch), and correlates signals across Entra ID, Microsoft Defender, Exchange, and Intune in a single unified pipeline. Threat intelligence from Microsoft TI, CISA KEV, and sector-specific feeds is built into every alert. This is enterprise-grade architecture — the same infrastructure used by Fortune 500 organisations — available to UK SMEs from £15/user/month.
Q.How does the AI threat intelligence work?
Our AI threat intelligence integrates multiple real-time data sources: (1) Microsoft Threat Intelligence — trillions of signals daily from 1.4+ billion Windows devices; (2) CISA KEV database — every alert cross-referenced against actively exploited CVEs in the wild; (3) Microsoft Defender Threat Intelligence — adversary TTPs, IOCs, and threat actor profiles; (4) Entra ID Identity Protection — real-time risk events including leaked credentials, unfamiliar sign-in properties, and token theft; (5) Microsoft Sentinel Fusion rules — multi-stage attack detection that correlates low-fidelity signals across data sources; (6) Custom sector-specific feeds for financial services, legal, healthcare, and public sector. Every alert is enriched with TI context before a human analyst sees it — so analysts spend time investigating, not gathering context.
Q.What data sources does the AI SOC platform ingest?
The platform ingests telemetry from: Microsoft Entra ID (all sign-ins, audit logs, identity protection events, conditional access, MFA, privilege changes); Microsoft Defender for Endpoint (threat detections, device risk scores, advanced hunting); Microsoft Defender for Office 365 (email threats, phishing, malware, suspicious URLs); Exchange Online (mail flow anomalies, mailbox access patterns); Microsoft Intune (device compliance, enrollment events, policy changes); and Azure Monitor (sign-in logs, audit logs, activity logs). All ingested via native Microsoft Graph API with read-only permissions — no agents, no log collectors, no network sensors.
Q.How fast are alerts generated and investigated?
Alerts are generated in under 60 seconds from the triggering event. The AI engine ingests telemetry in real time via Microsoft Graph API streaming, analyses it against learned behavioural baselines and threat intelligence feeds, and fires an alert immediately when an anomaly is detected. The alert — enriched with full attack-chain context — is then queued for UK-based SOC analyst investigation, typically picked up within minutes, 24/7/365. This compares to traditional MSSP models where batch SIEM processing introduces 5–30 minute delays before an alert is even visible.
Q.Do I need to deploy agents or infrastructure?
No. Coreitech's AI SOC platform uses native Microsoft Graph API integration with read-only permissions. There are no agents to deploy, no SIEM appliances to install, no log collectors to configure, and no network sensors to place. If your organisation uses Microsoft 365 (Exchange Online, Teams, SharePoint, Entra ID), the platform can begin ingesting telemetry within 24 hours of authorisation — simply grant the required Graph API permissions. For organisations using Google Workspace or non-Microsoft identity providers, contact us to discuss integration options.
Q.How does automated response work?
When the AI detects a confirmed threat, pre-built response playbooks can execute containment actions automatically within your environment: force user sign-out, revoke active sessions, reset credentials, disable accounts, quarantine devices, and revoke OAuth grants. Playbooks include human approval gates for high-impact actions (e.g., disabling an executive's account) and automatic execution for time-critical actions (e.g., revoking a session from a known malicious IP). Every action is logged with full audit trail. Response actions are agreed with you in advance via an incident response playbook — critical when minutes matter during an active attack.
Q.What is the difference between an AI SOC and a traditional MSSP?
A traditional MSSP (Managed Security Service Provider) deploys a SIEM appliance on your network, requires agents and log collectors, processes events in batches (5–30 minute delays), generates raw alerts without context, charges per-GB of ingestion plus per-alert plus per-analyst-hour, and often uses offshore analysts. Coreitech's AI SOC uses native Microsoft Graph API integration (zero infrastructure), processes events in real-time streaming (<60 second alerts), correlates and enriches alerts with AI and threat intelligence (90%+ fewer false positives), includes UK-based analyst investigation of every alert, offers automated playbook response, and charges a simple per-user fee from £15/user/month with no hidden costs.
Q.How much does the AI SOC platform cost?
AI SOC platform pricing starts from £15/user/month and includes: real-time telemetry ingestion across Entra ID, Defender, Exchange, and Intune; AI-powered threat correlation and behavioural baselining; threat intelligence enrichment from Microsoft TI, CISA KEV, and sector feeds; 24/7/365 UK-based human analyst investigation of every flagged alert; automated response playbooks; and monthly reporting. For a 50-user business that's £750/month — compared to £500,000+ annually for an in-house 3-analyst SOC providing only business-hours coverage. Contact us for a tailored quote based on your environment size, sector, and required response SLAs.
See the AI SOC Platform
in action
Book a 30-minute demo. We'll connect to your Microsoft tenant and show you real-time telemetry ingestion, AI threat correlation, and automated response playbooks — live.